<h1>Zero Trust Security Architecture Explained</h1>
<p>Zero Trust security architecture is revolutionizing how organizations protect their digital assets in an increasingly complex threat landscape. Unlike traditional perimeter-based security models, Zero Trust operates on a fundamental principle: never trust, always verify. This <a href="/article/pellet-guns-in-protests-a-comprehensive-guide-to-their-use-impact-and-the-call-for-regulation" title="Pellet Guns in Protests: A Comprehensive Guide to Their Use, Impact, and the Call for Regulation" class="internal-link">comprehensive guide</a> explores the core concepts, implementation strategies, and benefits of Zero Trust architecture.</p>
<h2>What Is Zero Trust Security?</h2>
<p>Zero Trust is a security framework that eliminates the concept of trusted internal networks versus untrusted external networks. Instead, it treats every user, device, and application as potentially hostile, regardless of their location or network connection. Every access request must be authenticated, authorized, and continuously validated before granting access to any resources.</p>
<blockquote>Zero Trust is not a single product or solution but rather a holistic <a href="/article/understanding-microservices-architecture-a-modern-approach-to-scalable-software-development" title="Understanding Microservices Architecture: A Modern Approach to Scalable Software Development" class="internal-link">approach to</a> security that combines multiple technologies and principles.</blockquote>
Advertisement
Loading partner content...
<h3>The Core Principles of Zero Trust</h3>
<ul>
<li><b>Verify Explicitly</b> - Always authenticate and authorize based on all available data points</li>
<li><b>Use Least Privilege Access</b> - Limit user access rights to only what is necessary</li>
<li><b>Assume Breach</b> - Design systems with the assumption that attackers are already inside</li>
<li><b>Microsegmentation</b> - Divide networks into small zones to contain potential breaches</li>
<li><b>Continuous Monitoring</b> - Constantly verify and assess trust levels</li>
</ul>
<h2>Why Zero Trust Matters in Today's Digital Landscape</h2>
<p>The traditional castle-and-moat security model has become obsolete in the face of <a href="/article/serverless-computing-benefits-revolutionizing-modern-application-development" title="Serverless Computing Benefits: Revolutionizing Modern Application Development" class="internal-link">modern</a> threats. With the rise of cloud computing, remote work, and sophisticated cyberattacks, organizations need a more robust security framework. Zero Trust addresses these challenges by providing:</p>
<ol>
<li><b>Enhanced Security Posture</b> - Reduces attack surface and limits lateral movement</li>
<li><b>Improved Compliance</b> - Helps meet regulatory requirements through granular access control</li>
<li><b>Better Visibility</b> - Provides comprehensive monitoring of all network activities</li>
<li><b>Reduced Risk</b> - Minimizes the impact of potential breaches</li>
<li><b>Support for Remote Work</b> - Enables secure access from anywhere</li>
</ol>
Advertisement
Loading partner content...
<h2>Key Components of Zero Trust Architecture</h2>
<h3>Identity and Access <a href="/article/mastering-time-management-a-self-help-guide-for-indian-professionals" title="Mastering Time Management: A Self-Help Guide for Indian Professionals" class="internal-link">Management</a> (IAM)</h3>
<p>Identity forms the foundation of Zero Trust. Robust IAM systems implement multi-factor authentication, single sign-on, and identity federation to ensure only legitimate users gain access. Role-based access control (RBAC) and attribute-based access control (ABAC) further refine permissions based on user characteristics and context.</p>
<h3>Microsegmentation</h3>
<p>Network microsegmentation divides the network into isolated segments, each with its own security controls. This approach limits lateral movement by attackers and contains potential breaches. Software-Defined Perimeter (SDP) technology creates dynamic, one-to-one connections between users and resources, making the network invisible to unauthorized users.</p>
Advertisement
Loading partner content...
<h3>Continuous Monitoring and Analytics</h3>
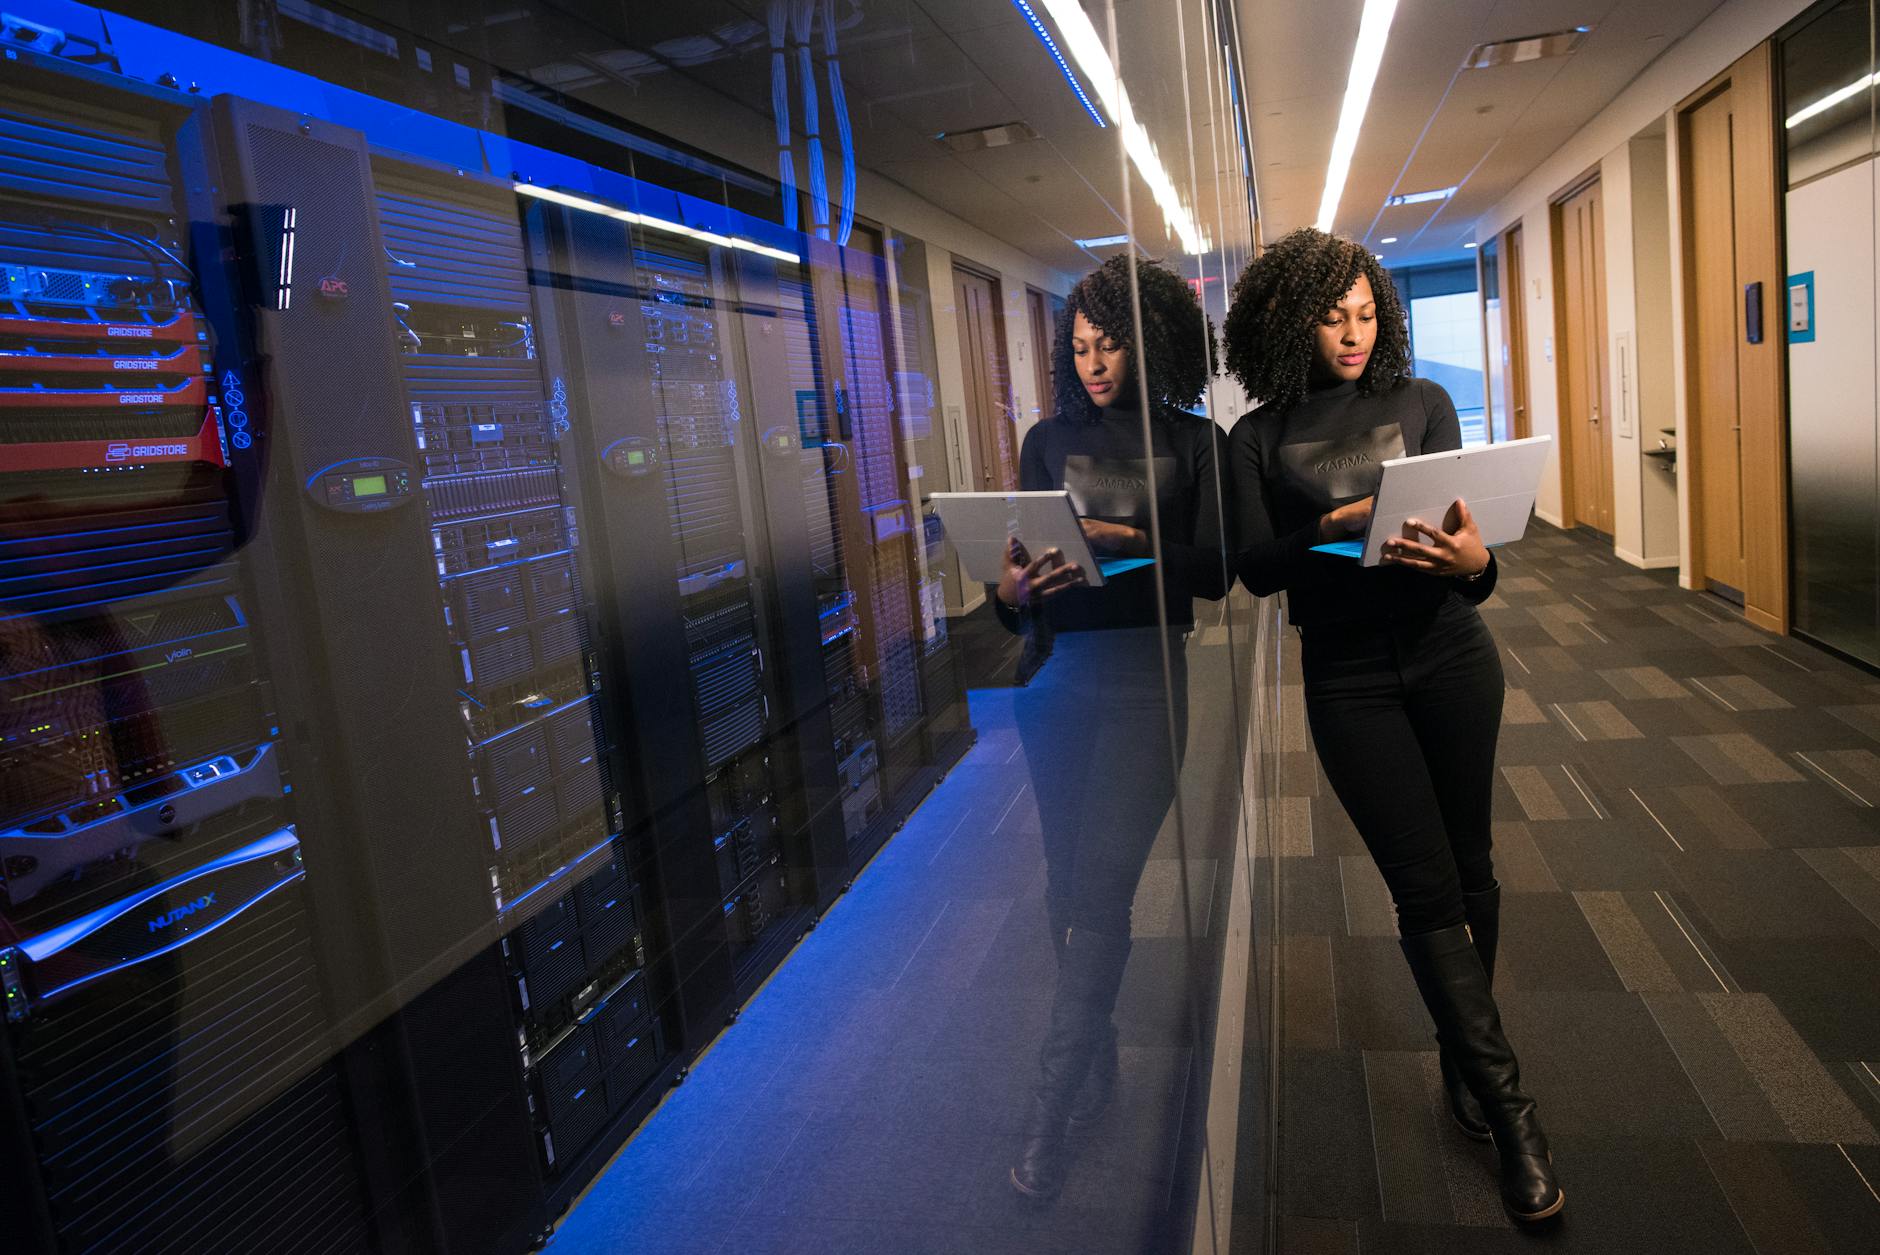
<p>Real-time monitoring and analytics are essential for detecting anomalies and potential threats. Security Information and Event Management (SIEM) systems, User and Entity Behavior Analytics (UEBA), and Security Orchestration, Automation, and Response (SOAR) tools provide the intelligence needed to make informed access decisions.</p>
<h3>Device Security</h3>
<p>Endpoint security ensures that devices accessing the network meet security standards. Device health checks, patch management, and endpoint detection and response (EDR) solutions verify that devices are secure before granting access. Mobile Device Management (MDM) and Unified Endpoint Management (UEM) solutions help enforce security policies across all device types.</p>
<h2>Implementing Zero Trust: A Phased Approach</h2>
Advertisement
Loading partner content...
<h3>Phase 1: Define the Protect Surface</h3>
<p>Start by identifying your critical assets, data, <a href="/article/demystifying-web3-how-decentralized-applications-are-reshaping-india-s-digital-future" title="Demystifying Web3: How Decentralized Applications Are Reshaping India's Digital Future" class="internal-link">applications</a>, and services (collectively known as the protect surface). This focused approach is more manageable than trying to secure the entire attack surface. Map the transaction flows of your protect surface to understand how data moves through your environment.</p>
<h3>Phase 2: Design a Zero Trust Network</h3>
<p>Create a network architecture that supports Zero Trust principles. Implement microsegmentation to isolate sensitive resources. Deploy next-generation firewalls and secure web gateways to control traffic flow. Establish secure connectivity through VPNs or SDP solutions.</p>
<h3>Phase 3: Establish Policies</h3>
Advertisement
Loading partner content...
<p>Develop comprehensive access policies based on the Kipling Method: who, what, when, where, why, and how. Implement the principle of least privilege to minimize access rights. Create policies for different user types, device types, and resource types.</p>
<h3>Phase 4: Monitor and Maintain</h3>
<p>Implement continuous monitoring to detect and respond to threats in real-time. Use analytics to identify unusual patterns and potential breaches. Regularly review and update policies based on changing threats and business needs. Conduct periodic security assessments to ensure the effectiveness of your Zero Trust implementation.</p>
<h2>Zero Trust in Action: Real-World Applications</h2>
<h3>Remote Work Security</h3>
Advertisement
Loading partner content...
<p>Zero Trust enables secure remote work by verifying users and devices regardless of location. It provides secure access to corporate resources without requiring a traditional VPN connection. Conditional access policies ensure that only compliant devices can access sensitive data.</p>
<h3>Cloud Security</h3>
<p>Cloud environments benefit significantly from Zero Trust principles. By implementing identity-based access control and microsegmentation, organizations can secure their cloud workloads and data. Zero Trust extends security beyond the corporate network to include cloud services and applications.</p>
<h3>DevOps and CI/CD Pipelines</h3>
<p>Zero Trust enhances DevOps security by implementing strict access controls for development and deployment environments. It ensures that only authorized developers can access specific resources and that code deployments follow secure practices. Continuous verification of build environments prevents supply chain attacks.</p>
Advertisement
Loading partner content...
<h2>Challenges and Considerations</h2>
<p>Implementing Zero Trust requires significant planning and resources. Organizations must consider:</p>
<ul>
<li><b>Complexity</b> - Zero Trust involves multiple technologies and processes</li>
<li><b>Legacy Systems</b> - Older systems may not support modern authentication methods</li>
<li><b>User Experience</b> - Security measures must balance protection with usability</li>
<li><b>Cost</b> - Implementation requires investment in technology and expertise</li>
<li><b>Cultural Change</b> - Organizations must shift from perimeter-based thinking</li>
</ul>
<h2>The Future of Zero Trust</h2>
<p>As cyber threats evolve, Zero Trust continues to advance. Artificial intelligence and machine learning are enhancing threat detection and response capabilities. The integration of Zero Trust with other security frameworks, such as Secure Access Service Edge (SASE), is creating more comprehensive security solutions. Zero Trust is becoming the standard for organizations of all sizes as they recognize the need for adaptive, context-aware security.</p>
Advertisement
Loading partner content...
<p>Zero Trust security architecture represents a fundamental shift in how organizations approach cybersecurity. By eliminating implicit trust and implementing continuous verification, Zero Trust provides a more resilient defense against modern threats. While implementation requires careful planning and resources, the benefits of enhanced security, improved compliance, and better risk management make Zero Trust an essential strategy for organizations navigating today's complex digital landscape.</p>
<figure class="my-8 overflow-hidden rounded-3xl shadow-xl">
<img src="https://images.pexels.com/photos/36498362/pexels-photo-36498362.png?auto=compress&cs=tinysrgb&dpr=2&h=650&w=940" alt="pexels" class="w-full h-[400px] object-cover" />
<figcaption class="mt-2 text-center text-sm text-gray-500 italic">pexels</figcaption>
</figure>
<figure class="my-8 overflow-hidden rounded-3xl shadow-xl">
<img src="https://images.pexels.com/photos/36498362/pexels-photo-36498362.png?auto=compress&cs=tinysrgb&dpr=2&h=650&w=940" alt="pexels" class="w-full h-[400px] object-cover" />
<figcaption class="mt-2 text-center text-sm text-gray-500 italic">pexels</figcaption>
</figure></b></i></i></i>